Advisory services
Programs that survive contact with the business.
Governance that gets ignored is worse than none at all. We design controls your teams will follow and your auditors will accept.
What we do
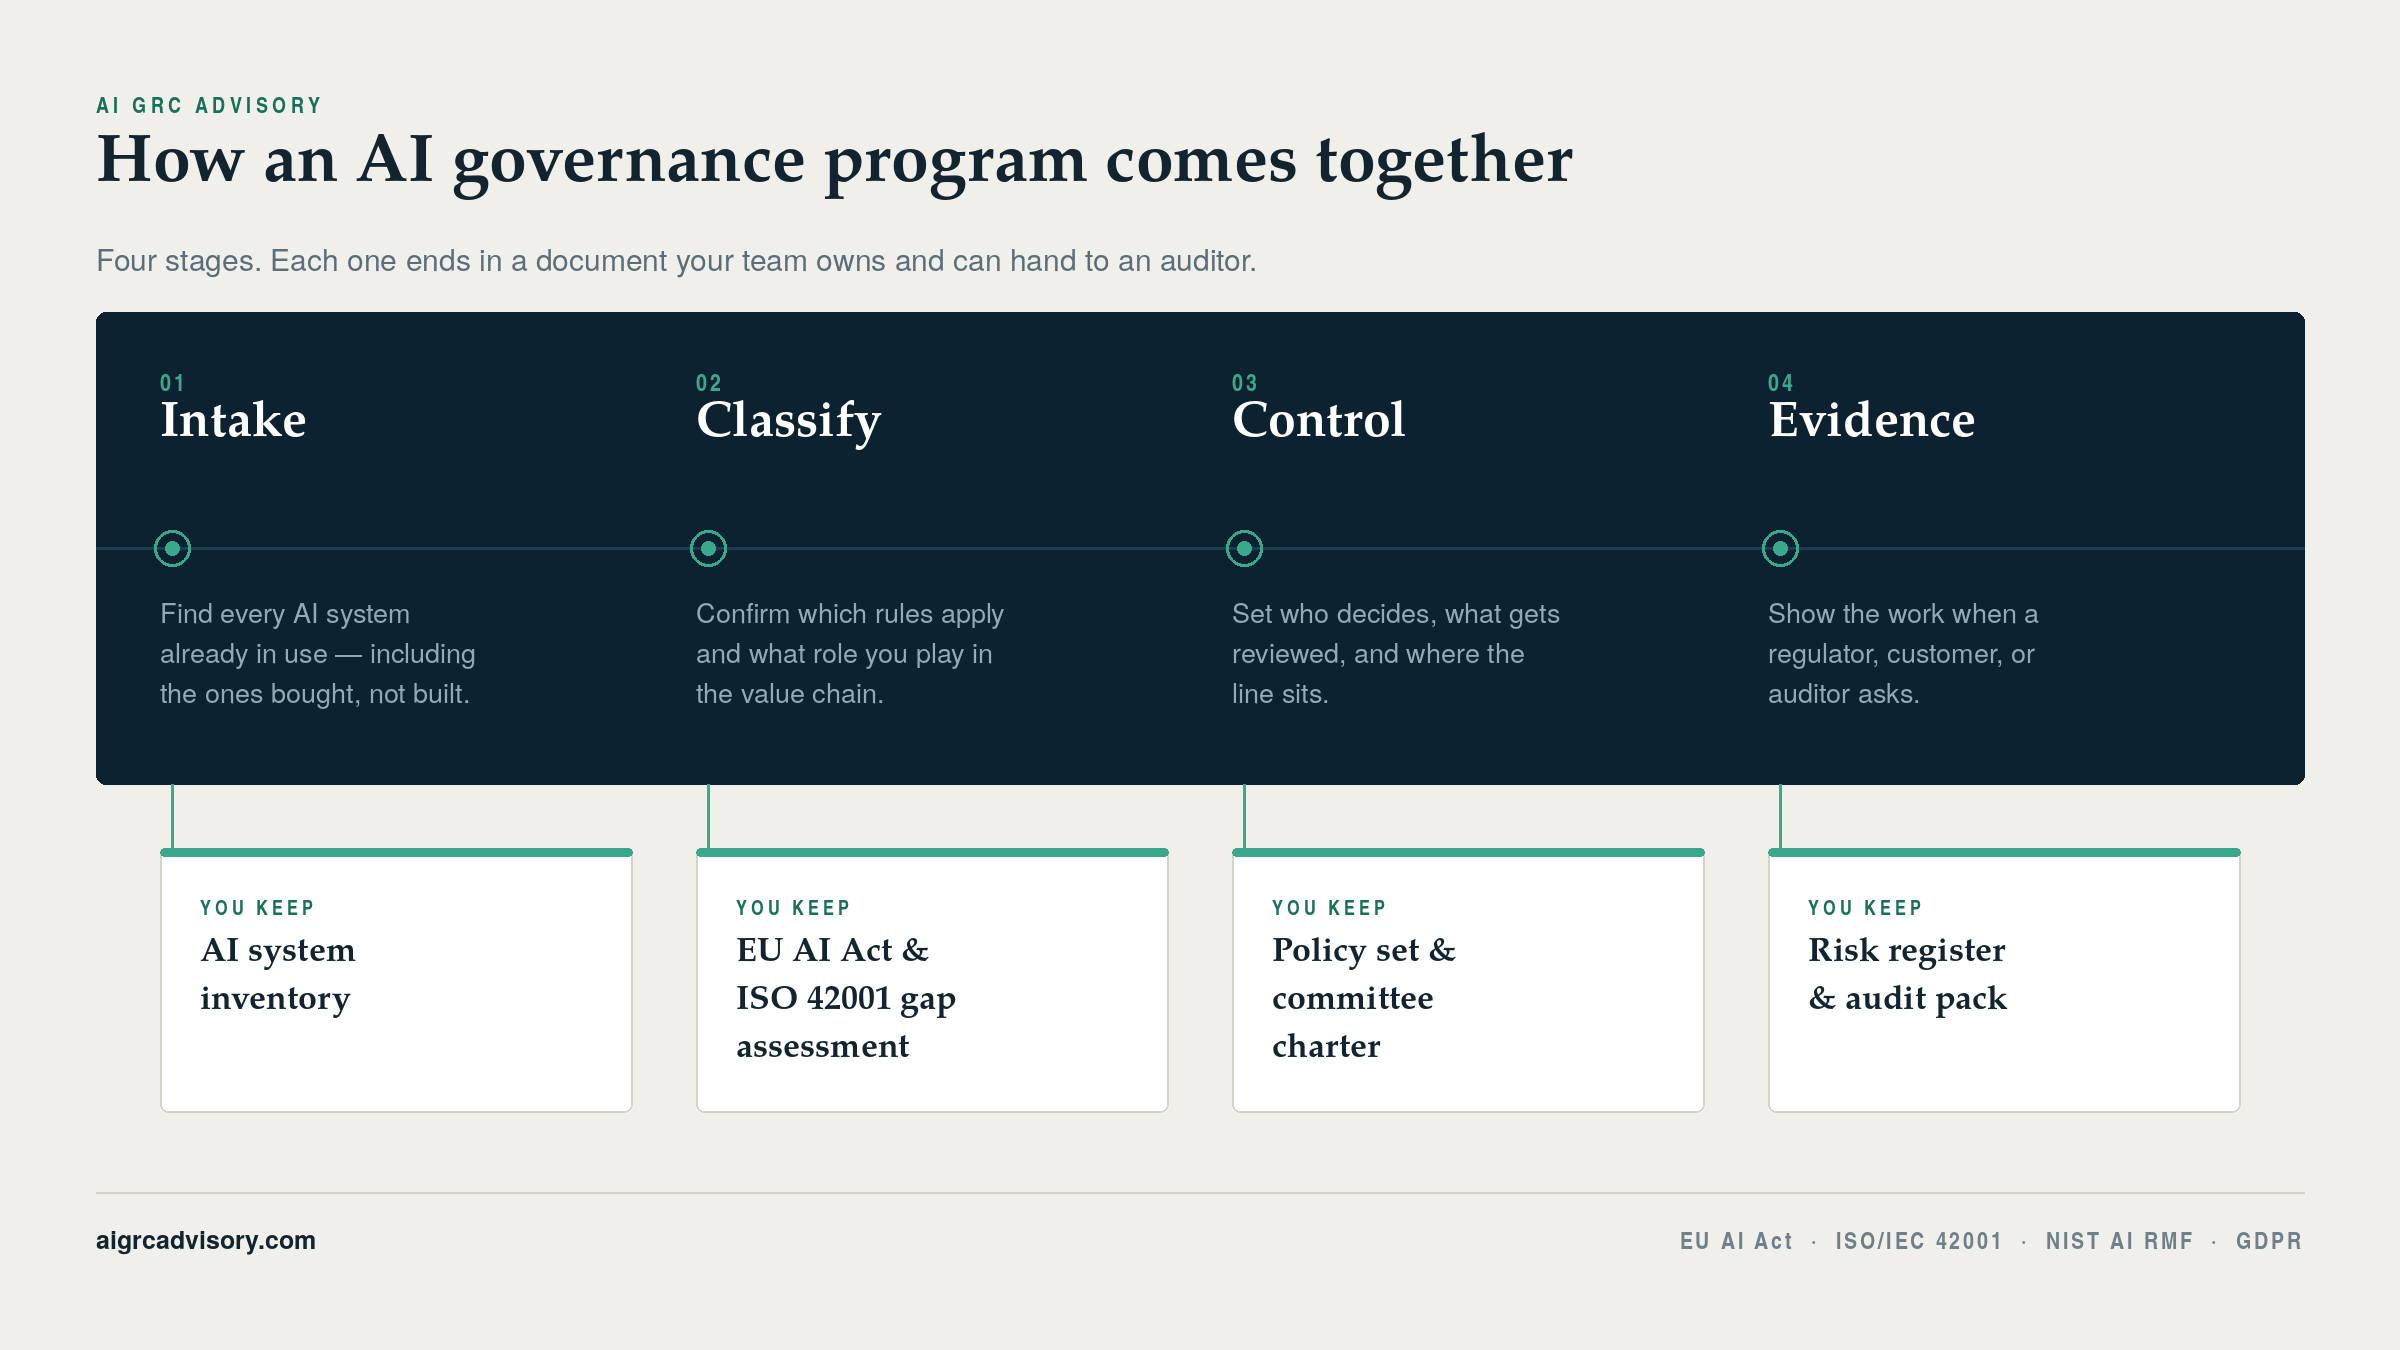
Each engagement ends with documents your team owns — not a slide deck.
AI governance frameworks
Operating model, roles, intake process, and the committee structure that keeps decisions moving.
AI risk assessments
Identify and rank AI risk across systems and third-party tools, with mitigations mapped to owners.
Regulatory readiness
Classify your systems, confirm your role in the value chain, and close the gaps before enforcement reaches you.
Privacy and AI
Lawful basis, DPIAs for AI systems, data minimization, and training-data provenance.
Vendor and procurement review
Questionnaires, contract clauses, and a review workflow that does not stall the deal.
Fractional AI governance lead
Monthly support: model intake, exception reviews, board reporting, and regulatory monitoring.
Four steps, four to eight weeks
Scope
Free 30-minute call, then a written scope with fixed price and dates. No open-ended hours.
Discover
Interviews, system inventory, and a review of what documentation already exists.
Assess and draft
Gap analysis against your chosen framework, plus the policies and registers to close it.
Hand over
Working session with your team, a prioritized roadmap, and 30 days of follow-up questions.
Handling Controlled Unclassified Information or preparing for CMMC? That work is delivered through cyberdsc.com.
Next step
Start with a scoping call.
Bring your current state, however messy. You leave with a written view of your top priorities.